Plenty of security failures don't start with a clever hack. They start with a risk nobody owned. We see this gap in many companies. Tools get bought and policies get written, yet no single manager answers for the whole picture. The Certified Information Security Manager credential was built to close that gap. Here, you'll see how CISM supports cybersecurity risk management at the enterprise level, and whether it fits your career.
What Is the Certified Information Security Manager (CISM) Certification?
CISM comes from ISACA, the same body behind CISA and CRISC. It targets people who manage security programs, not just run tools. More than 107,000 professionals have earned it since 2002, according to ISACA.
The CISM certification is proof that you can tie security work to business decisions. It covers four domains: governance, risk management, the security program, and incident management. The exam has 150 multiple-choice questions and runs four hours. You need 450 on a scale of 200 to 800 to pass.
Here's a timing note: ISACA updates the exam outline on November 3, 2026. The four domains stay, but you'll see new content on enterprise architecture and information security architecture.
Ways CISM Supports Enterprise Cybersecurity Risk Management
CISM doesn't hand you a tool. It gives you a way of thinking and working. Here are the main ways it helps inside a real company.
It Puts Someone in Charge of Cyber Risk
Governance is where it starts. CISM teaches you to set security strategy, define roles, and give every risk a named owner. When ownership is clear, risks stop falling between teams. Leaders also know who to ask when something looks off.
Teaches a Repeatable Cybersecurity Risk Assessment
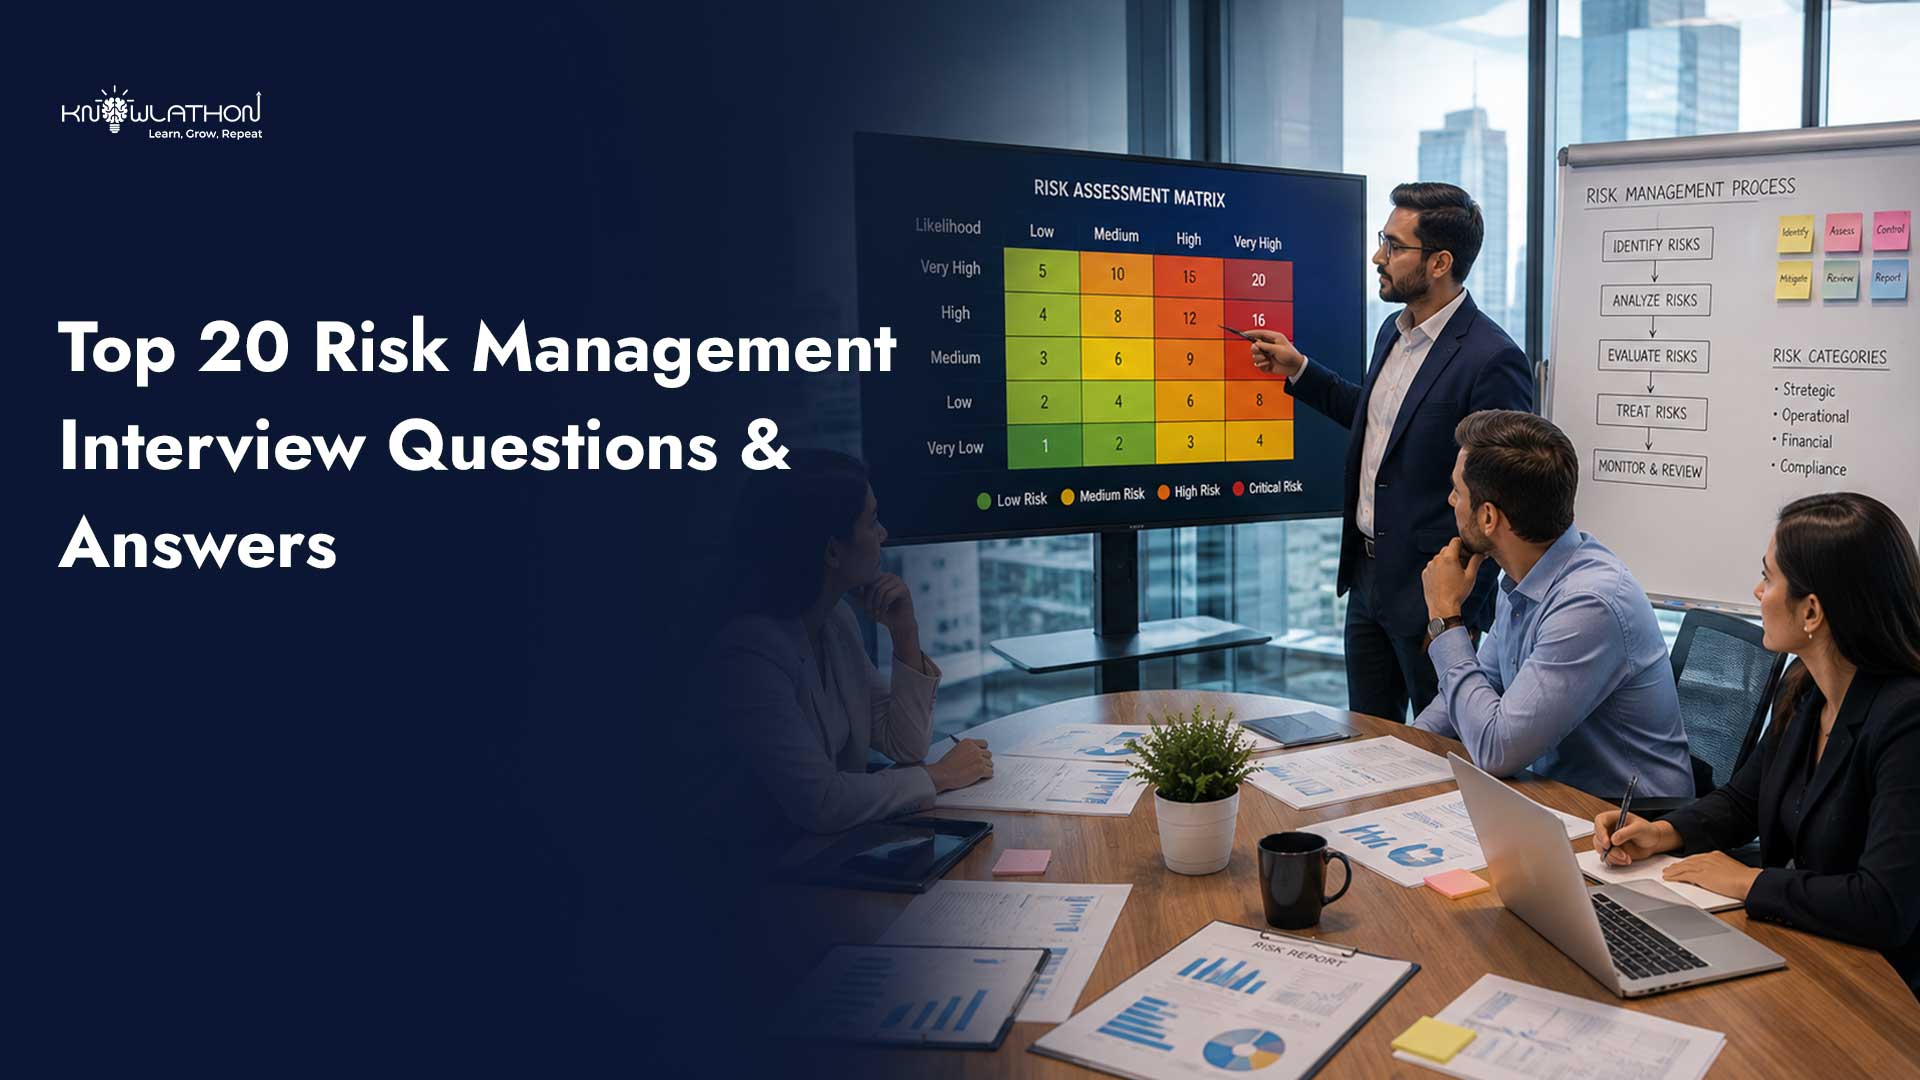
A CISM-trained manager treats cybersecurity risk assessment as a process, not a one-time audit. You list assets, threats, and weak spots, including those sitting with third parties. Then you rate each risk by likelihood and business impact. The result is a ranked list you can defend in front of executives.
Gives You Clear Ways to Treat Risk
Finding risk is only half the job. You also pick a response: mitigate, transfer, avoid, or accept it. CISM stresses naming an owner for each risk and each control, then monitoring both over time. That keeps decisions from going stale after the first meeting.
Ties Cyber Risk to Business Goals and Risk Appetite
Risk appetite is how much risk your leaders will accept to hit their goals. A CISM professional works inside that limit and speaks in business terms, like downtime cost or possible fines. That makes it easier to win budget. It also keeps cybersecurity and risk management tied to company strategy.
Builds Compliance Into Daily Work
Laws, regulations, and contract terms all shape your controls. CISM trains you to map those requirements to what you actually do. Gaps then show up early, not during an audit. You also learn to hold vendors to the same standards you set for yourself.
Prepares You for Incidents and Business Continuity
Even good prevention fails once in a while. What happens next decides how much damage you take. CISM covers incident response plans, business impact analysis, business continuity, and disaster recovery. You learn to classify incidents, contain them, and run a post-incident review.
Feeds Cyber Risk Into Enterprise Risk Management
Enterprise risk management looks at every threat to the business, and cyber risk is now a big slice. CISM teaches you to report security risks to leadership in plain language. Lessons from each incident flow back into your risk register. That loop keeps enterprise risk management honest.
CISM vs CISSP vs CRISC for Risk-Focused Careers
These three get compared a lot. They aim at different jobs.
- CISM: Best if you lead a security program and report to executives.
- CISSP: Comes from ISC2 and covers a wide technical and managerial range.
- CRISC: Also from ISACA, and centered on IT risk and controls.
Many people stack them over time. Start with the one that matches the job you want in two years.
Why Choose Knowlathon for CISM Training
At Knowlathon, we build our CISM training around how managers actually work. You get field examples and scenario practice, not just slides. We cover all four domains and keep our material tied to the current exam outline.
We also train teams, so your company can build its own security leadership bench. Not sure when to book your exam? Talk to us, and we'll help you pick a date.